

Try Free and Start Using Realistic Verified MS-102 Dumps Instantly
MS-102 Actual Questions - Instant Download 550 Questions
NEW QUESTION # 268
You have an Azure AD tenant that contains the users shown in the following table.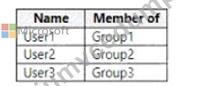
Your company uses Microsoft Defender for Endpoint. Microsoft Defender for Endpoint contains the roles shown in the following table.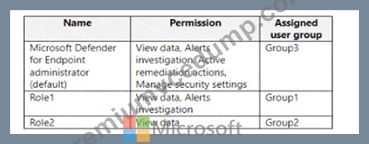
Microsoft Defender for Endpoint contains the device groups shown in the following table.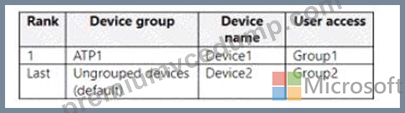
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE; Each correct selection is worth one point.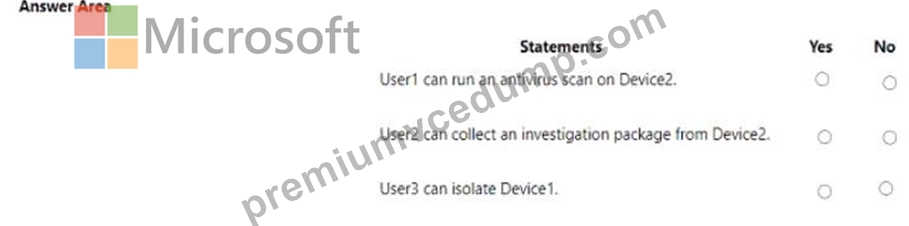
Answer:
Explanation: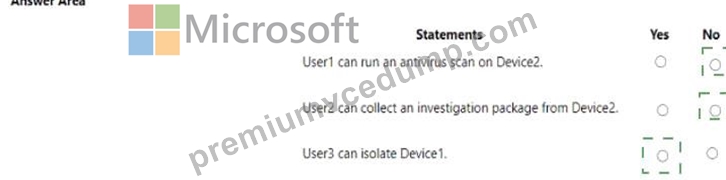
Explanation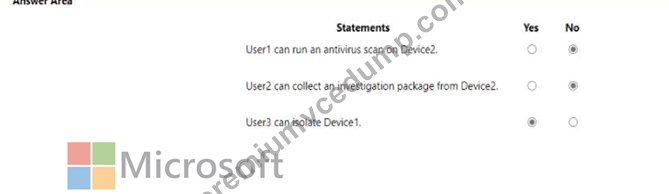
NEW QUESTION # 269
You have a Microsoft 365 E5 tenant that contains the users shown in the following table.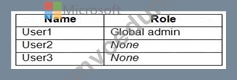
You provision the private store in Microsoft Store for Business.
You assign Microsoft Store for Business roles to the users as shown in the following table.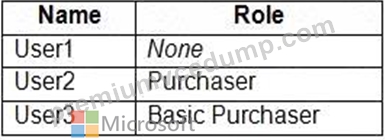
You need to identify which users can add apps to the private store, and which users can assign apps from Microsoft Store for Business.
Which users should you identify? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.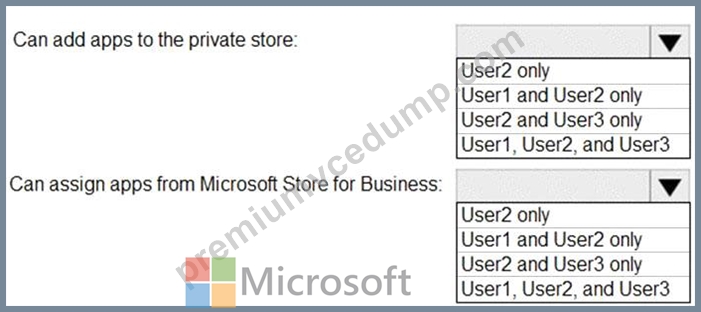
Answer:
Explanation: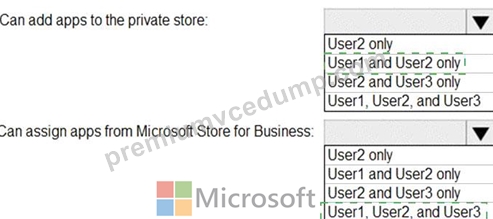
Explanation
Graphical user interface, text, application Description automatically generated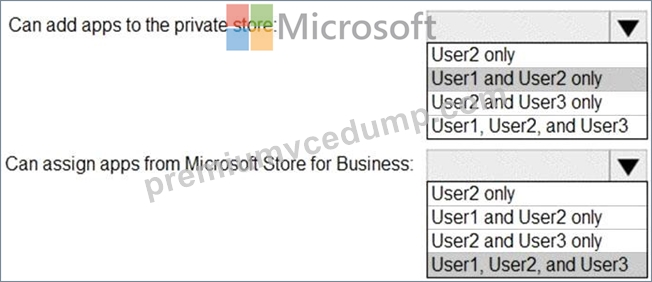
Reference:
https://docs.microsoft.com/en-us/microsoft-store/roles-and-permissions-microsoft-store-for-business
https://docs.microsoft.com/en-us/education/windows/education-scenarios-store-for-business#basic-purchaser-rol
NEW QUESTION # 270
You need to configure Office on the web to meet the technical requirements.
What should you do?
- A. Enable sensitivity labels for Office files in SharePoint Online and OneDrive.
- B. Configure an auto-labeling policy to apply the sensitivity labels.
- C. Assign the Office apps admin role to User1.
- D. Assign the Global reader role to User1.
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/sensitivity-labels-sharepoint-onedrive-files?view=o365-worldwide
NEW QUESTION # 271
HOTSPOT
You have a new Microsoft 365 E5 tenant.
Enable Security defaults is set to Yes.
A user signs in to the tenant for the first time.
Which multi-factor authentication (MFA) method can the user use, and how many days does the user have to register for MFA? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.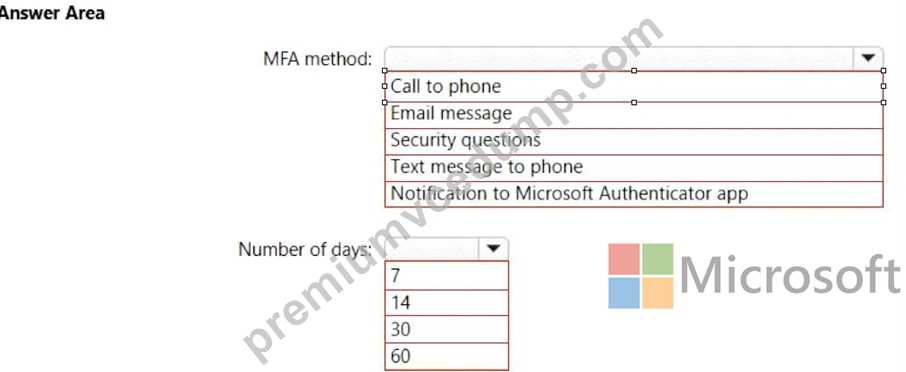
Answer:
Explanation: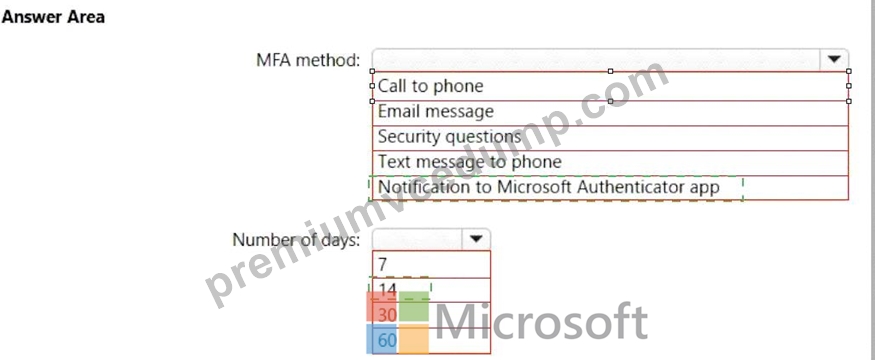
Explanation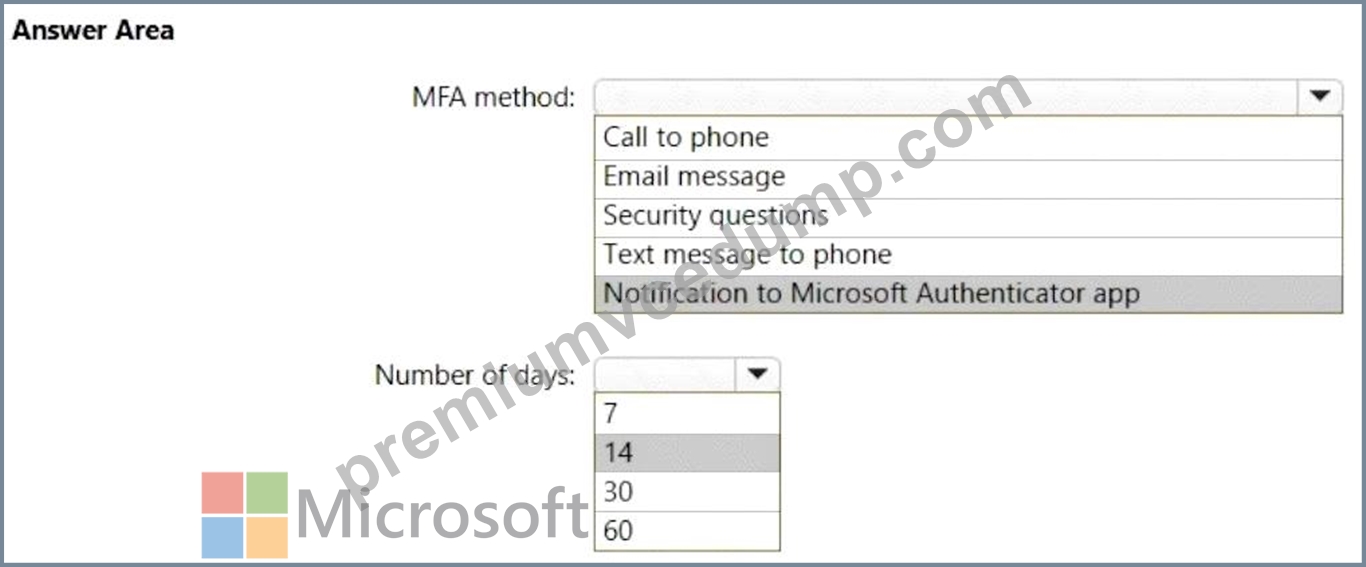
Box 1: Notification to Microsoft Authenticator app
Do users have 14 days to register for Azure AD Multi-Factor Authentication?
Users have 14 days to register for MFA with the Microsoft Authenticator app from their smart phones, which begins from the first time they sign in after security defaults has been enabled. After 14 days have passed, the user won't be able to sign in until MFA registration is completed.
Box 2: 14
Azure AD Identity Protection will prompt your users to register the next time they sign in interactively and they'll have 14 days to complete registration. During this 14-day period, they can bypass registration if MFA isn't required as a condition, but at the end of the period they'll be required to register before they can complete the sign-in process.
Reference:
https://learn.microsoft.com/en-us/microsoft-365/solutions/empower-people-to-work-remotely-secure-sign-in
https://learn.microsoft.com/en-us/azure/active-directory/identity-protection/howto-identity-protection-configure-
NEW QUESTION # 272
You have a Microsoft 365 E5 tenant that contains five devices enrolled in Microsoft Intune as shown in the following table.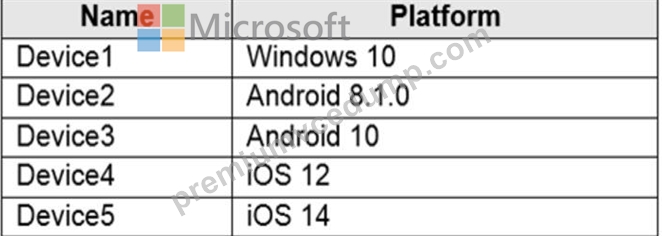
All the devices have an app named App1 installed.
You need to prevent users from copying data from App1 and pasting the data into other apps.
Which policy should you create in Microsoft Endpoint Manager, and what is the minimum number of required policies? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.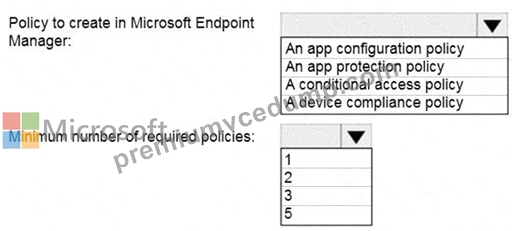
Answer:
Explanation: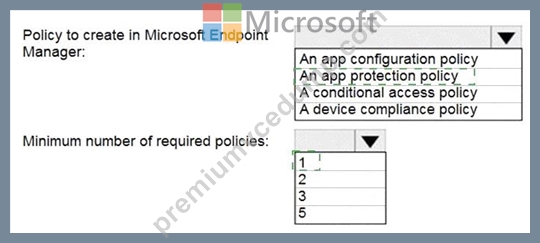
Explanation: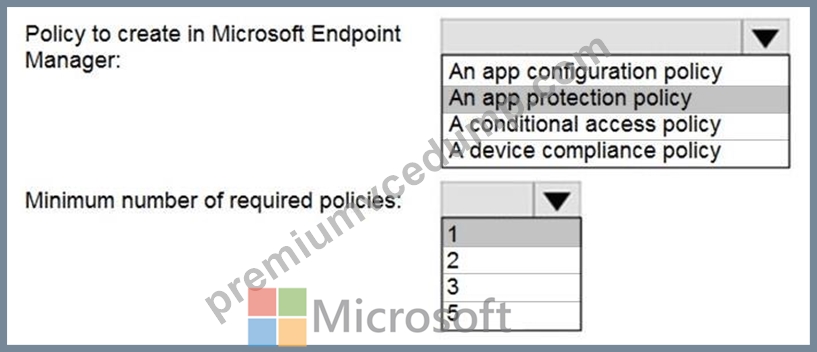
Reference:
https://docs.microsoft.com/en-us/mem/intune/apps/app-protection-policy
NEW QUESTION # 273
You have a Microsoft 365 ES subscription that has three auto retention policies as show in the following exhibit.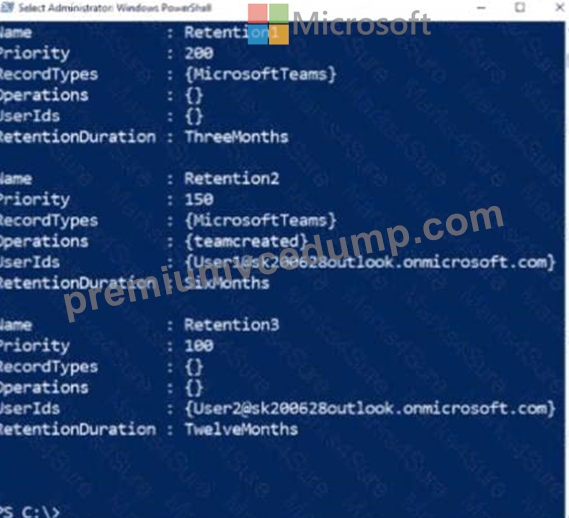
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic NOTE Each correct selection is worth one point.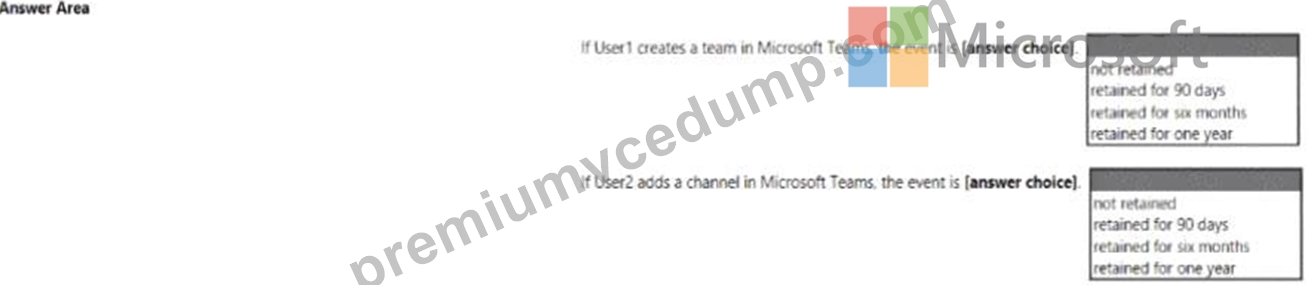
Answer:
Explanation: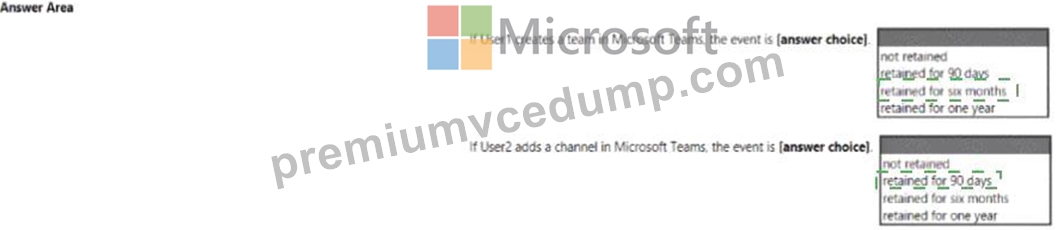
Explanation: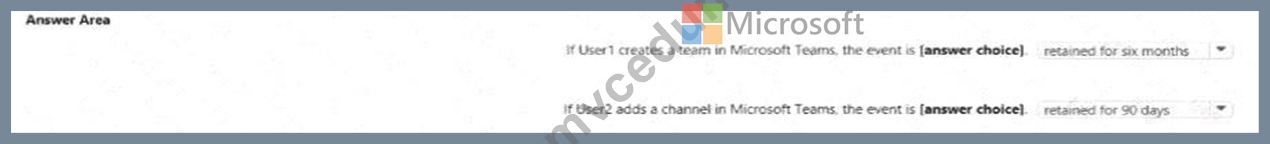
NEW QUESTION # 274
You have an Azure subscription and an on-premises Active Directory domain. The domain contains 50 computers that run Windows 10.
You need to centrally monitor System log events from the computers.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.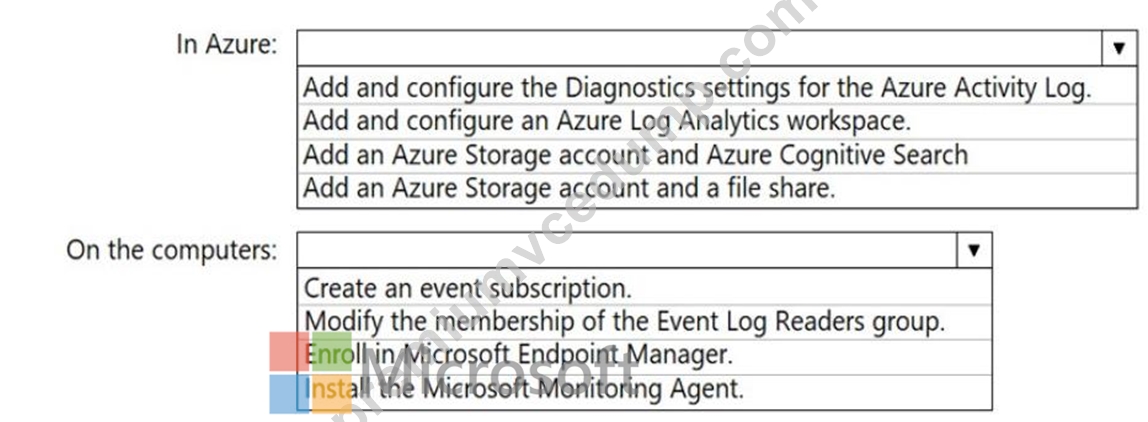
Answer:
Explanation: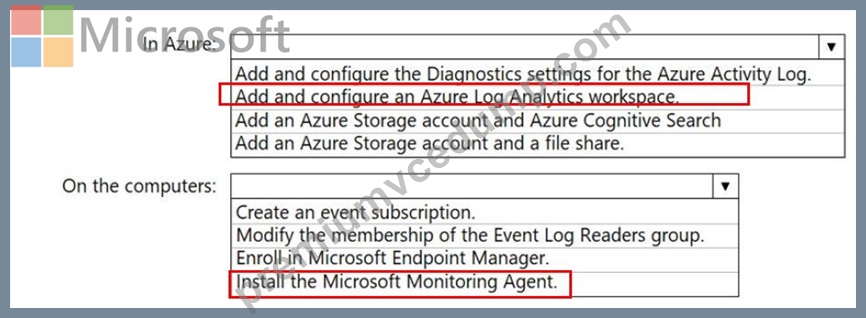
Reference:
https://docs.microsoft.com/en-us/azure/azure-monitor/learn/quick-collect-windows-computer
NEW QUESTION # 275
You have a Microsoft 365 E5 subscription.
All corporate Windows 11 devices are managed by using Microsoft Intune and onboarded to Microsoft Defender for Endpoint.
You need to meet the following requirements:
* View an assessment of the device configurations against the Center for Internet Security (CIS) vl.0.0 benchmark.
* Protect a folder named C:\Folder1 from being accessed by untrusted applications on the devices.
What should you do? To answer, select the appropriate options in the answer area.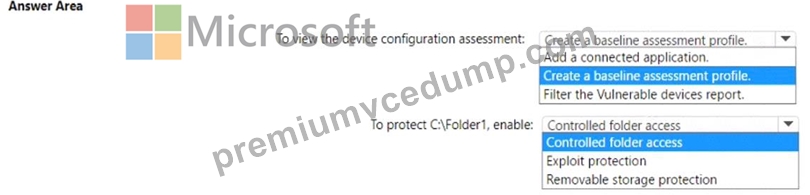
Answer:
Explanation: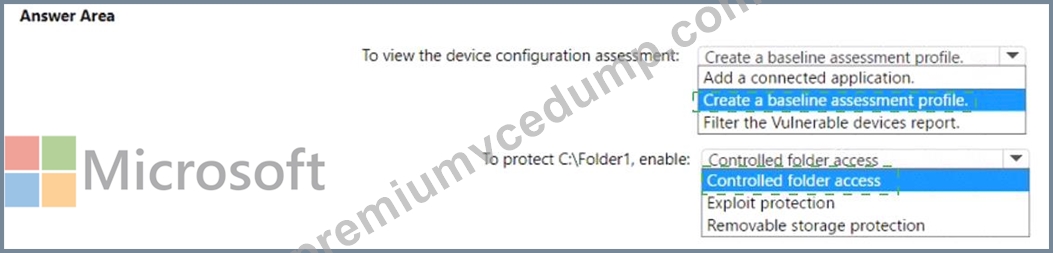
Explanation: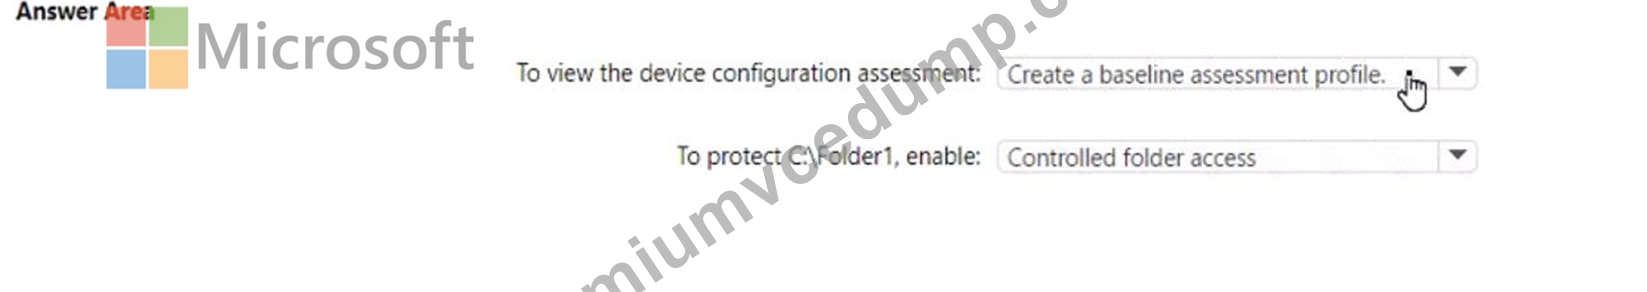
NEW QUESTION # 276
You have a Microsoft 365 E5 subscription that has Microsoft Defender for Endpoint integrated with Microsoft Endpoint Manager.
Devices are onboarded by using Microsoft Defender for Endpoint.
You plan to block devices based on the results of the machine risk score calculated by Microsoft Defender for Endpoint.
What should you create first?
- A. a device configuration policy
- B. a conditional access policy
- C. a device compliance policy
- D. an endpoint detection and response policy
Answer: C
Explanation:
Reference:
https://docs.microsoft.com/en-us/mem/intune/protect/advanced-threat-protection-configure
NEW QUESTION # 277
You have a Microsoft 365 E5 tenant that contains five devices enrolled in Microsoft Intune as shown in the following table.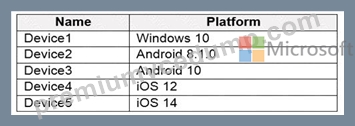
All the devices have an app named App1 installed.
You need to prevent users from copying data from App1 and pasting the data into other apps.
Which policy should you create in Microsoft Endpoint Manager, and what is the minimum number of required policies? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.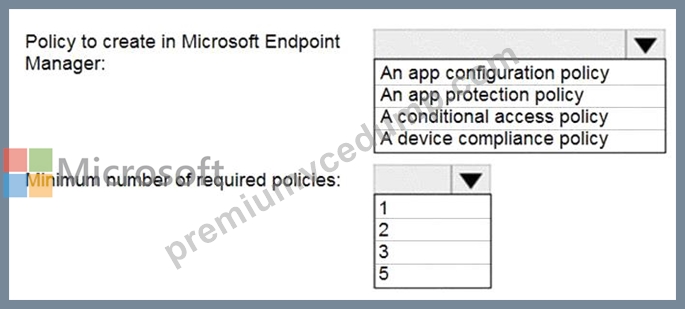
Answer:
Explanation: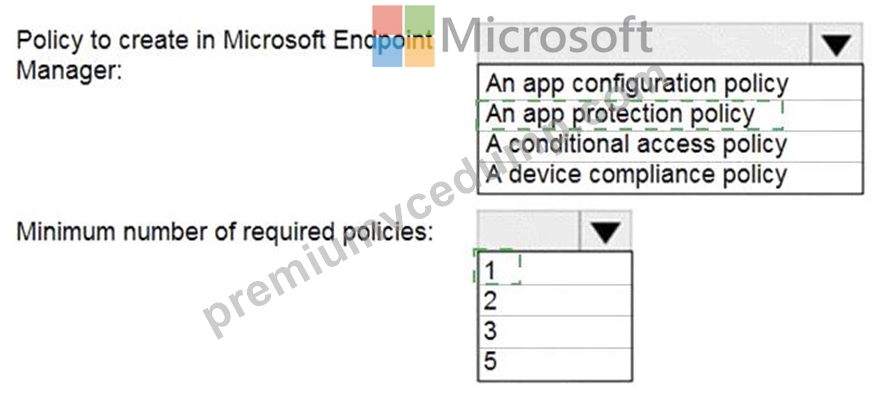
Explanation: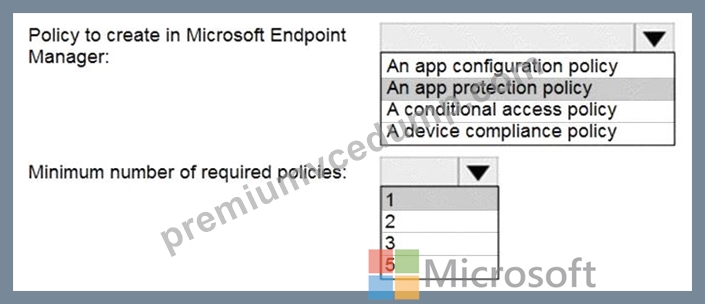
Reference:
https://docs.microsoft.com/en-us/mem/intune/apps/app-protection-policy
NEW QUESTION # 278
You have a Microsoft 365 E5 subscription that contains a user named User1.
The subscription has a single anti-malware policy as shown in the following exhibit.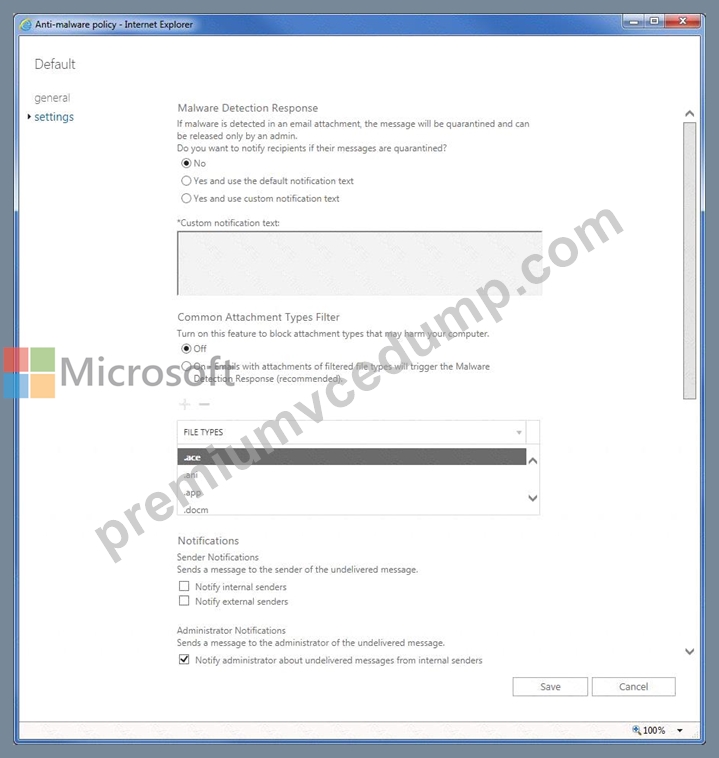
An email message that contains text and two attachments is sent to User1. One attachment is infected with malware.
How will the email message and the attachments be processed?
- A. The malware-infected attachment will be removed. The email message will be quarantined, and User1 will receive a copy of the message containing only the uninfected attachment.
- B. Both attachments will be removed. The email message will be quarantined, and User1 will receive a copy of the message containing the original text and a new attachment that includes the following text:
'Malware was removed." - C. Both attachments will be removed. The email message will be quarantined, and Used will receive an email message without any attachments and an email message that includes the following text: 'Malware was removed.'
- D. The email message will be quarantined, and the message will remain undelivered.
Answer: B
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/office-365-security/anti-malware-protection?view=o365
NEW QUESTION # 279
You have a Microsoft 365 E5 subscription and use Microsoft Defender for Endpoint. The subscription contains the devices shown in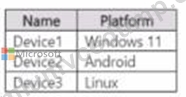
You need to create the Endpoint security policies shown in the following table.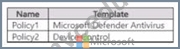
To which device can you apply each policy? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.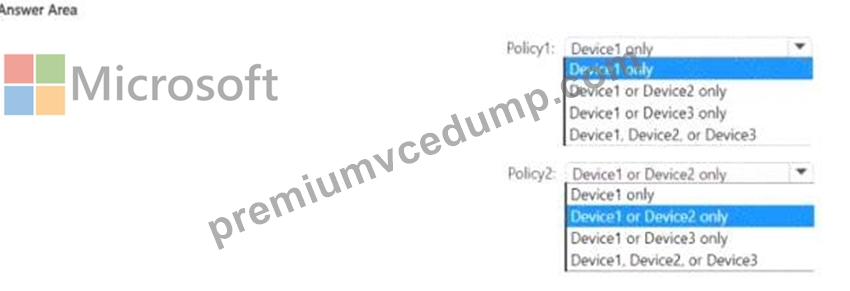
Answer:
Explanation: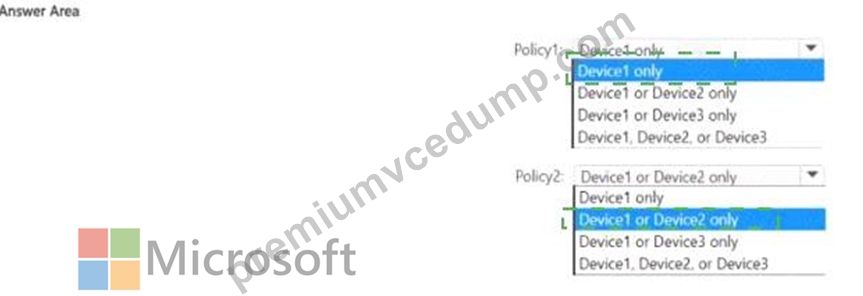
Explanation: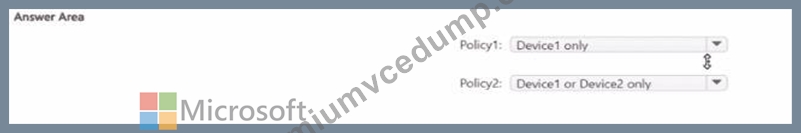
NEW QUESTION # 280
You have a Microsoft 365 E5 subscription that contains the devices shown in the following table.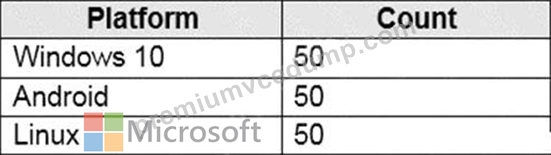
You need to configure an incident email notification rule that will be triggered when an alert occurs only on a Windows 10 device. The solution must minimize administrative effort.
What should you do first?
- A. From the Microsoft 365 Defender portal, create a device group.
- B. From the Microsoft 365 admin center, create a mail-enabled security group.
- C. From the Microsoft Endpoint Manager admin center, create a device category.
- D. From the Azure Active Directory admin center, create a dynamic device group.
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/defender-endpoint/machine-groups?view=o365- worldwide
https://docs.microsoft.com/en-us/microsoft-365/security/defender-endpoint/configure-email-notifications?
view=o365-worldwide
NEW QUESTION # 281
You have a Microsoft 365 tenant that contains devices enrolled in Microsoft Intune. The devices are configured as shown in the following table.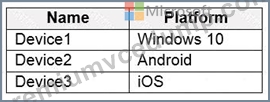
You plan to perform the following device management tasks in Microsoft Endpoint Manager:
Deploy a VPN connection by using a VPN device configuration profile.
Configure security settings by using an Endpoint Protection device configuration profile.
You support the management tasks.
What should you identify? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.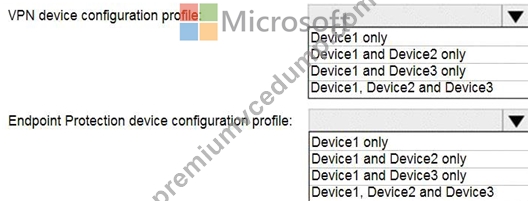
Answer:
Explanation: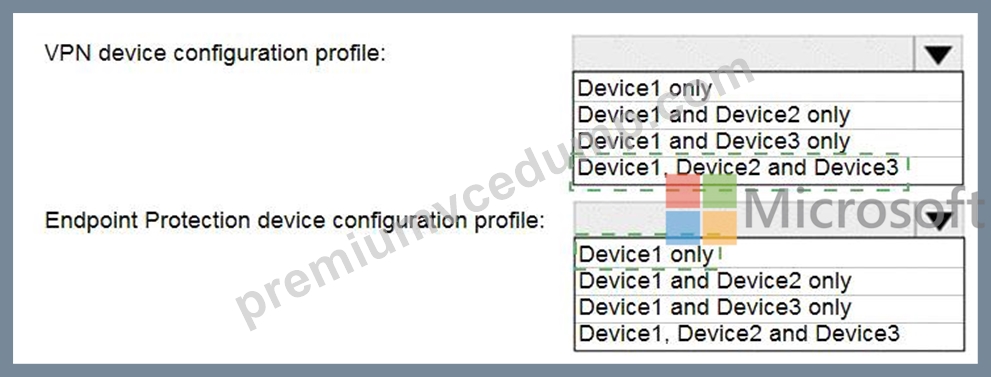
Explanation
Graphical user interface, application Description automatically generated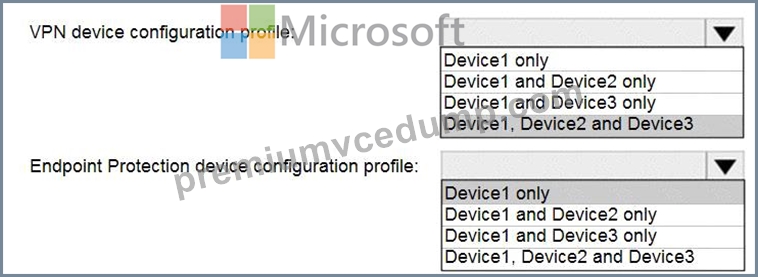
Reference:
https://docs.microsoft.com/en-us/mem/intune/configuration/vpn-settings-configure
https://docs.microsoft.com/en-us/mem/intune/protect/endpoint-protection-macos
NEW QUESTION # 282
You need to meet the compliance requirements for the Windows 10 devices.
What should you create from the Intune admin center?
- A. a device configuration profile
- B. a device compliance policy
- C. an application policy
- D. an app configuration policy
Answer: C
Explanation:
Topic 1, Contoso, Ltd
Overview
Contoso, Ltd. is a consulting company that has a main office in Montreal and two branch offices in Seattle and New York.
The company has the employees and devices shown in the following table.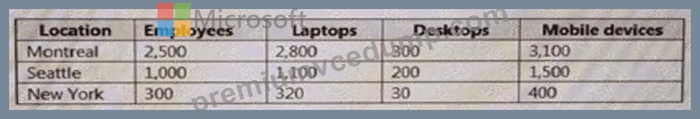
Contoso recently purchased a Microsoft 365 ES subscription.
Existing Environment
Requirement
The network contains an on-premises Active Directory forest named contoso.com. The forest contains the servers shown in the following table.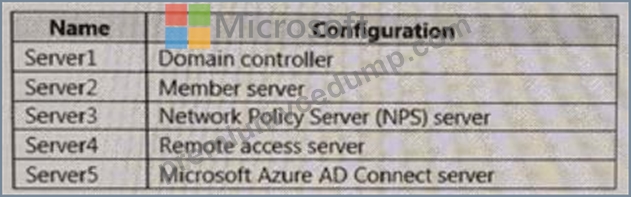
All servers run Windows Server 2016. All desktops and laptops are Windows 10 Enterprise and are joined to the domain.
The mobile devices of the users in the Montreal and Seattle offices run Android. The mobile devices of the users in the New York office run iOS.
The domain is synced to Azure Active Directory (Azure AD) and includes the users shown in the following table.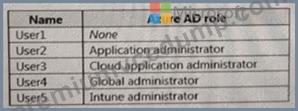
The domain also includes a group named Group1.
Planned Changes
Contoso plans to implement the following changes:
*Implement Microsoft 365.
*Manage devices by using Microsoft Intune.
*Implement Azure Advanced Threat Protection (ATP).
*Every September, apply the latest feature updates to all Windows computers. Every March, apply the latest feature updates to the computers in the New York office only.
Technical Requirements
Contoso identifies the following technical requirements:
*When a Windows 10 device is joined to Azure AD, the device must enroll in Intune automaticity.
*Dedicated support technicians must enroll all the Montreal office mobile devices in Intune.
*User1 must be able to enroll all the New York office mobile devices in Intune.
*Azure ATP sensors must be installed and must NOT use port mirroring.
*Whenever possible, the principle of least privilege must be used.
*A Microsoft Store for Business must be created.
Compliance Requirements
Contoso identifies the following compliance requirements:
*Ensure that the users in Group1 can only access Microsoft Exchange Online from devices that are enrolled in Intune and configured in accordance with the corporate policy.
*Configure Windows Information Protection (W1P) for the Windows 10 devices.
NEW QUESTION # 283
You have an Azure subscription and an on-premises Active Directory domain. The domain contains 50 computers that run Windows 10.
You need to centrally monitor System log events from the computers.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.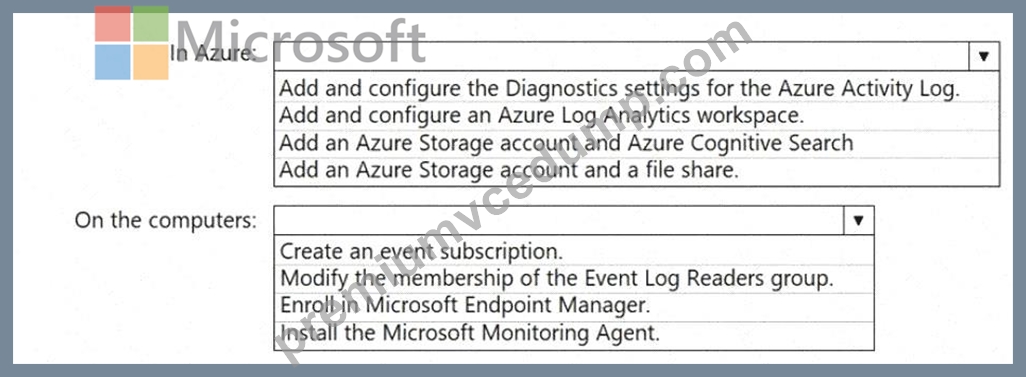
Answer:
Explanation: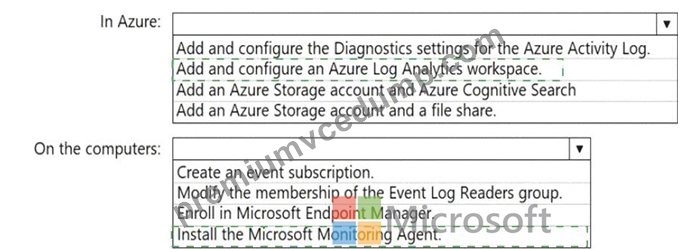
Explanation: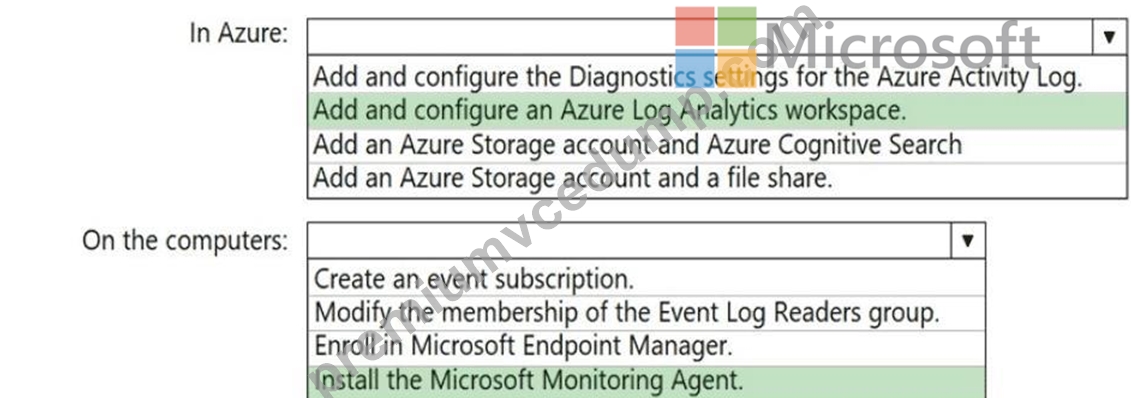
Reference:
https://docs.microsoft.com/en-us/azure/azure-monitor/learn/quick-collect-windows-computer
NEW QUESTION # 284
You have a Microsoft 365 E5 tenant.
You need to implement compliance solutions that meet the following requirements:
* Use a file plan to manage retention labels.
* Identify, monitor, and automatically protect sensitive information.
* Capture employee communications for examination by designated reviewers.
Which solution should you use for each requirement? To answer, drag the appropriate solutions to the correct requirements. Each solution may be used once, more than once, or not at all. You may need to drag the split bat between panes or scroll to view content.
NOTE: Each correct selection is worth one point.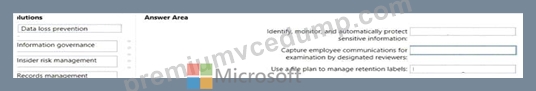
Answer:
Explanation: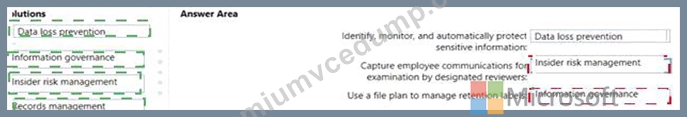
Explanation
Graphical user interface, text, application Description automatically generated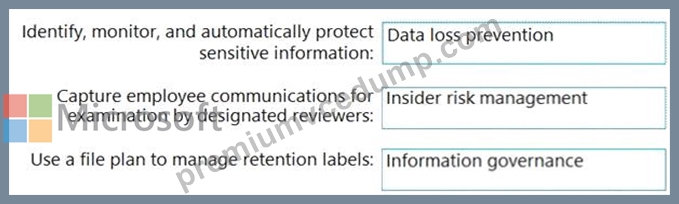
NEW QUESTION # 285
You have a Microsoft 365 subscription that contains the devices shown in the following table.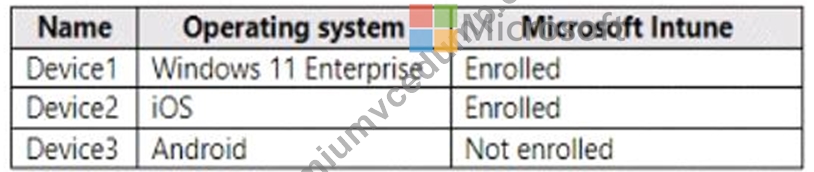
You install Microsoft Word on all the devices.
You plan to configure policies to meet the following requirements:
* Word files created by using Windows devices must be encrypted automatically.
* If an Android device becomes jailbroken, access to corporate data must be blocked from Word.
* For iOS devices, users must be prevented from using native or third-party mail clients to connect to Microsoft 365.
Which type of polio/ should you configure for each device? To answer, drag the appropriate policy types to the correct devices. Each policy type may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.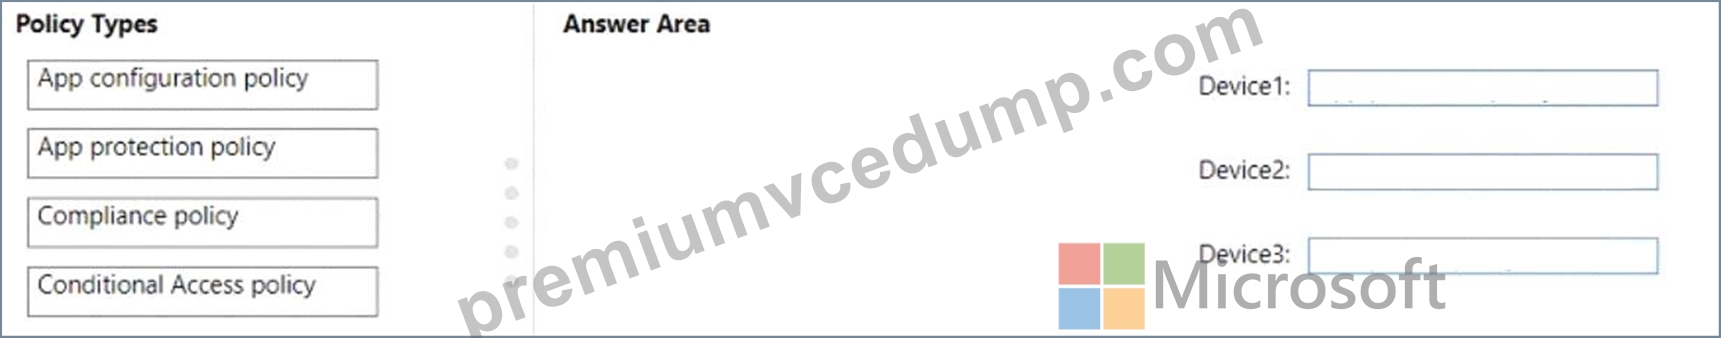
Answer:
Explanation: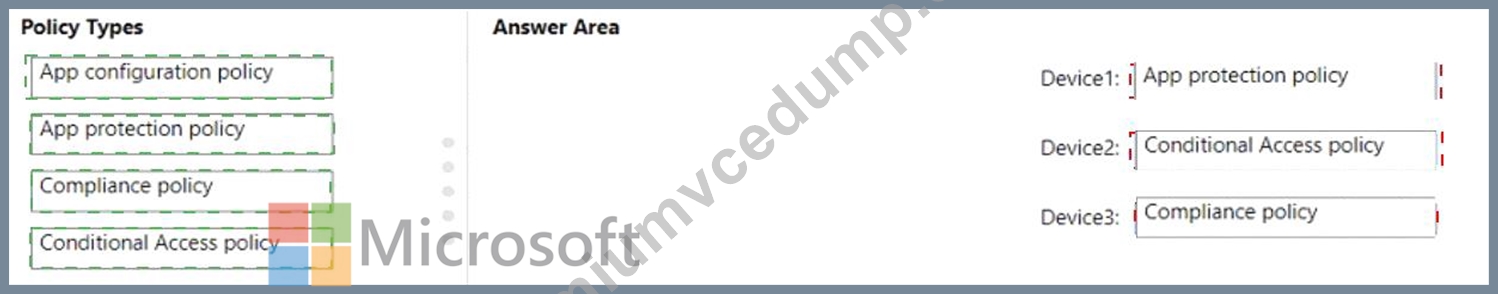
Explanation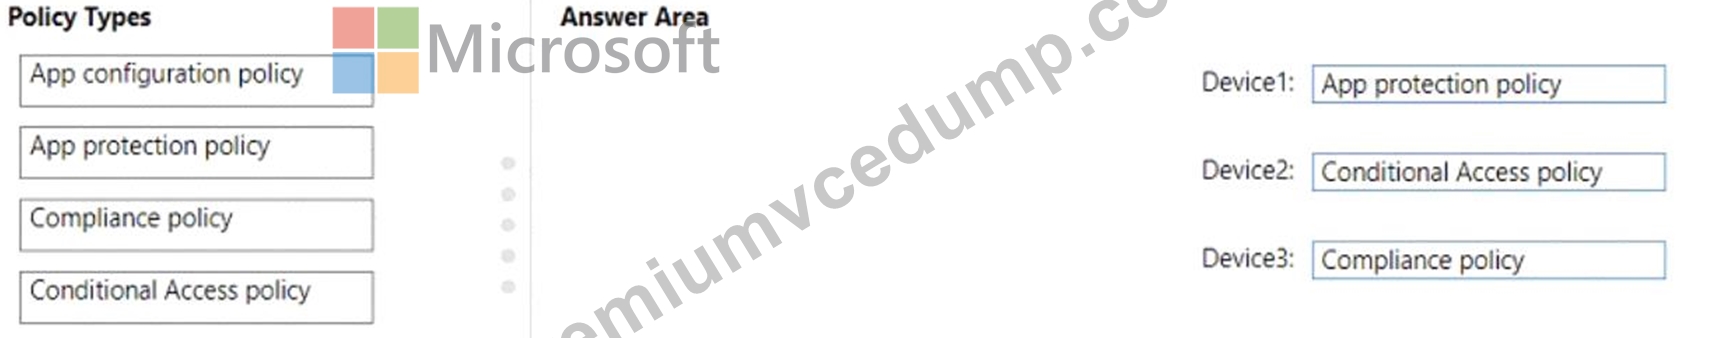
NEW QUESTION # 286
You have a Microsoft 365 subscription.
All uses are assigned Microsoft 365 Apps for enterprise licenses.
You need to ensure that reports display the names of users that have activated Microsoft 365 apps and on how many devices. What should you modify in the Microsoft 365 admin center?
- A. Organization information
- B. Org settings for Reports
- C. the Reports reader role
- D. Org settings for Privacy profile
Answer: B
NEW QUESTION # 287
You have a Microsoft 365 subscription.
You view the Service health Overview as shown in the following exhibit.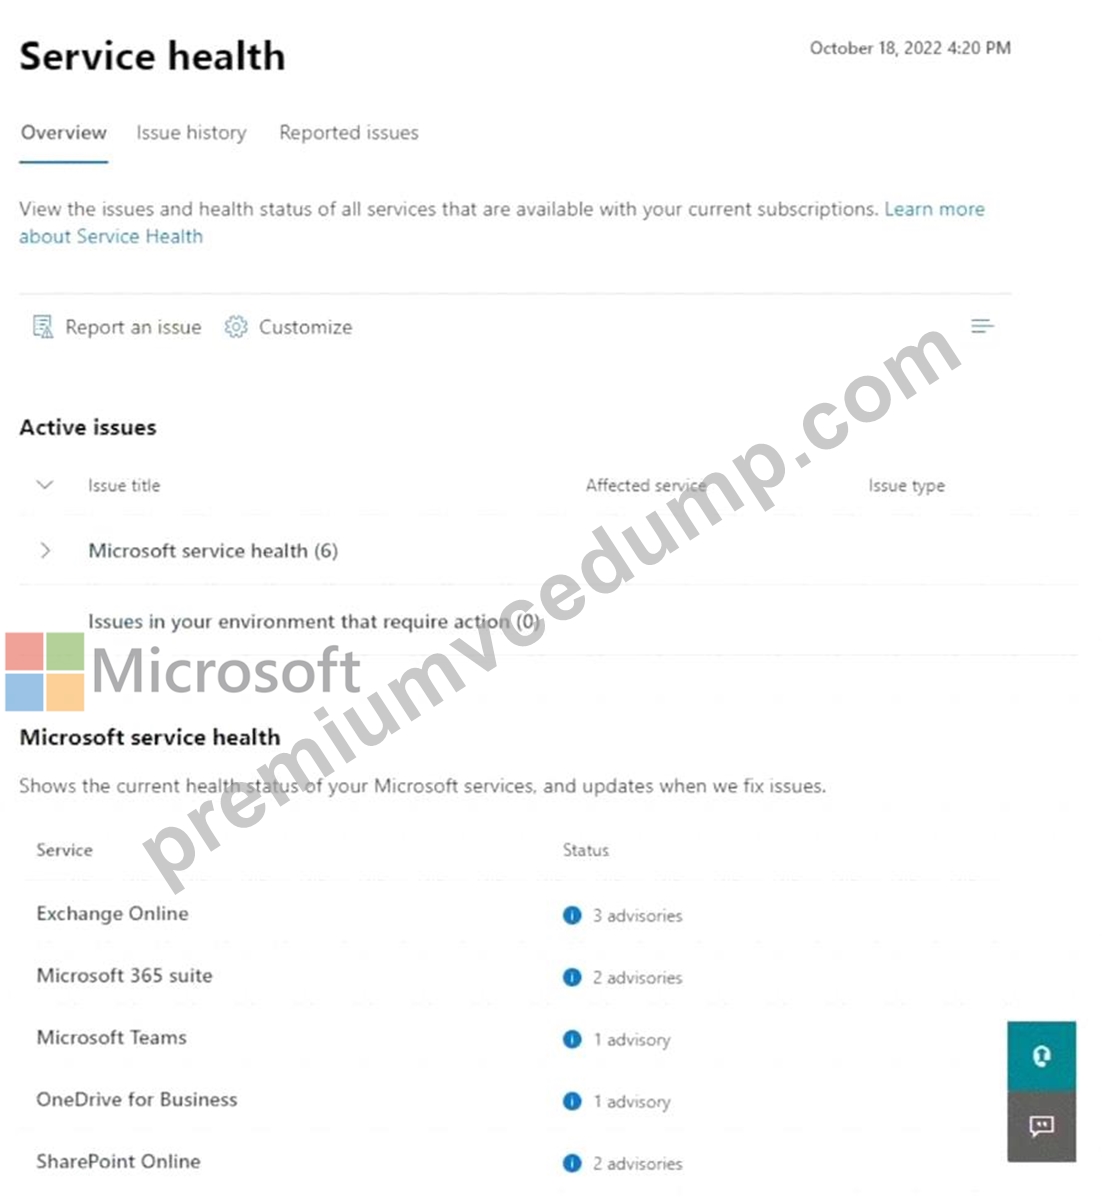
You need to ensure that a user named User1 can view the advisories to investigate service health issues.
Which role should you assign to User1?
- A. Compliance Administrator
- B. Reports Reader
- C. Service Support Administrator
- D. Message Center Reader
Answer: B
Explanation:
Explanation
Service Support admin
Assign the Service Support admin role as an additional role to admins or users who need to do the following in addition to their usual admin role:
- Open and manage service requests
- View and share message center posts
- Monitor service health
Incorrect:
* Message center reader
Assign the Message center reader role to users who need to do the following:
- Monitor message center notifications
- Get weekly email digests of message center posts and updates
- Share message center posts
- Have read-only access to Azure AD services, such as users and groups
* Reports reader
Assign the Reports reader role to users who need to do the following:
- View usage data and the activity reports in the Microsoft 365 admin center
- Get access to the Power BI adoption content pack
- Get access to sign-in reports and activity in Azure AD
- View data returned by Microsoft Graph reporting API
Reference:
https://learn.microsoft.com/en-us/microsoft-365/admin/add-users/about-admin-roles?view=o365-worldwide
NEW QUESTION # 288
You have a Microsoft 365 E5 tenant that contains the devices shown in the following table.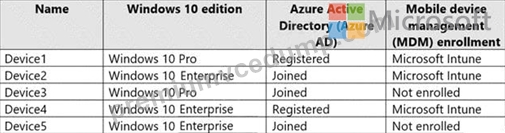
You add custom apps to the private store in Microsoft Store Business.
You plan to create a policy to show only the private store in Microsoft Store for Business.
To which devices can the policy be applied?
- A. Device2 and Device4 only
- B. Device2, Device3, and Device5 only
- C. Device2 only
- D. Device1 and Device3 only
- E. Device1, Device2, Device3, Device4, and Device5
Answer: A
NEW QUESTION # 289
You have an Azure AD tenant and a Microsoft 365 E5 subscription. The tenant contains the users shown in the following table.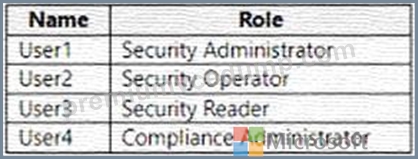
You plan to implement Microsoft Defender for Endpoint.
You verify that role-based access control (RBAC) is turned on in Microsoft Defender for Endpoint.
You need to identify which user can view security incidents from the Microsoft 365 Defender portal.
Which user should you identify?
- A. User1
- B. User3
- C. User4
- D. User2
Answer: A
NEW QUESTION # 290
You have a Microsoft 365 E5 subscription.
You need to configure Privileged Identity Management (PIM) for the User Administrator role in Microsoft Entr a. Eligible users must meet the following requirements:
* Always be able to request the User Administrator role.
* Must provide a reason when requesting the User Administrator role
* Must require multi-factor authentication (MFA} when activating the User Administrator role The solution must minimize administrative effort.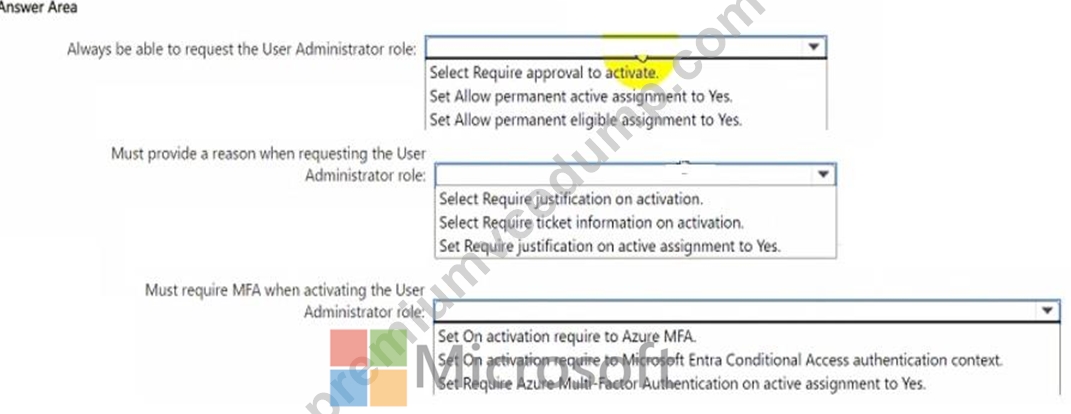
Answer:
Explanation: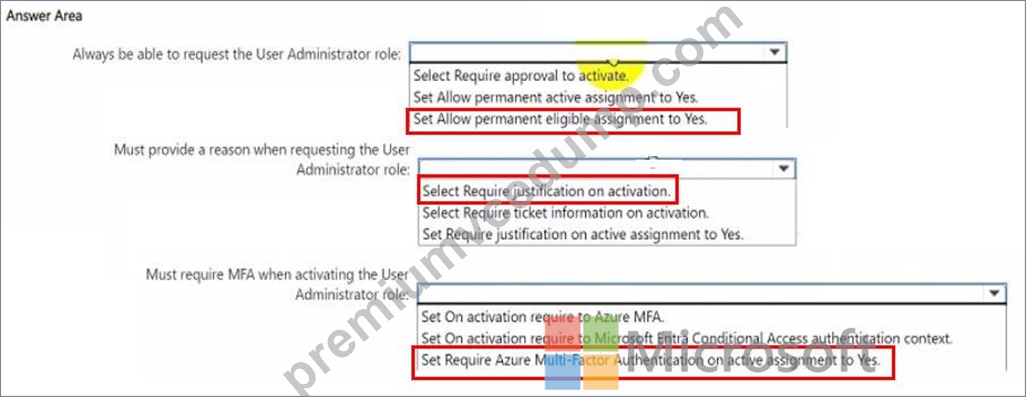
NEW QUESTION # 291
......
Microsoft MS-102 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
Download Free Latest Exam MS-102 Certified Sample Questions: https://pass4lead.premiumvcedump.com/Microsoft/valid-MS-102-premium-vce-exam-dumps.html