

Exam Passing Guarantee Dec 18, 2025 JN0-637 Exam with Accurate Quastions!
Test Engine to Practice Test for JN0-637 Valid and Updated Dumps
Juniper JN0-637 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
| Topic 6 |
|
| Topic 7 |
|
NEW QUESTION # 64
You have noticed a high number of TCP-based attacks directed toward your primary edge device.
You are asked to configure the IDP feature on your SRX Series device to block this attack.
Which two IDP attack objects would you configure to solve this problem? (Choose two.)
- A. host
- B. Network
- C. Protocol anomaly
- D. Signature
Answer: C,D
NEW QUESTION # 65
Exhibit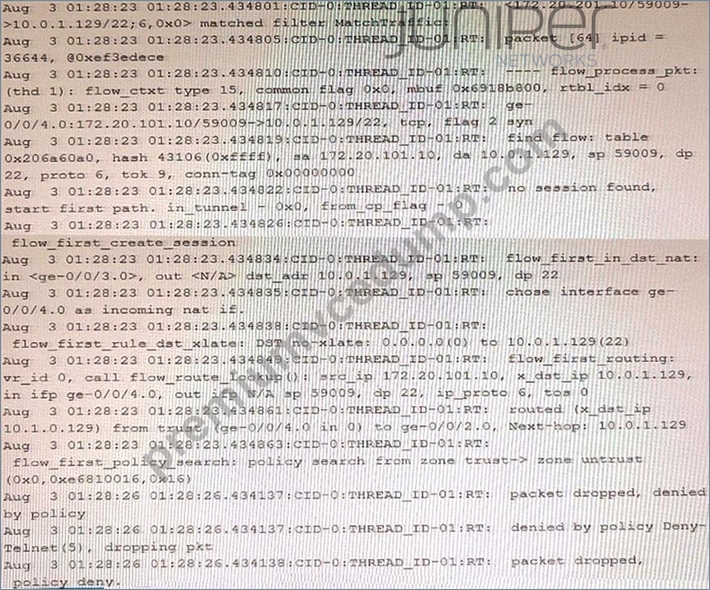
Which two statements are correct about the output shown in the exhibit. (Choose two.)
- A. The packet matches a user-configured policy
- B. The packet is an SSH packet
- C. The source address is translated.
- D. The destination address is translated.
Answer: B,C
NEW QUESTION # 66
You are asked to share threat intelligence from your environment with third party tools so that those tools can be identify and block lateral threat propagation from compromised hosts.
Which two steps accomplish this goal? (Choose Two)
- A. Configure application tokens in the Juniper ATP Cloud to limit who has access
- B. Enable SRX Series firewalls to share Threat intelligence with third party tool.
- C. Enable Juniper ATP Cloud to share threat intelligence
- D. Configure application tokens in the SRX Series firewalls to limit who has access
Answer: A,C
Explanation:
To share threat intelligence from your environment with third party tools, you need to enable Juniper ATP Cloud to share threat intelligence and configure application tokens in the Juniper ATP Cloud to limit who has access. The other options are incorrect because:
A) Configuring application tokens in the SRX Series firewalls is not necessary or sufficient to share threat intelligence with third party tools. Application tokens are used to authenticate and authorize requests to the Juniper ATP Cloud API, which can be used to perform various operations such as submitting files, querying C&C feeds, and managing allowlists and blocklists1. However, to share threat intelligence with third party tools, you need to enable the TAXII service in the Juniper ATP Cloud, which is a different protocol for exchanging threat information2.
D) Enabling SRX Series firewalls to share threat intelligence with third party tools is not possible or supported. SRX Series firewalls can send potentially malicious objects and files to the Juniper ATP Cloud for analysis and receive threat intelligence from the Juniper ATP Cloud to block malicious traffic3.
However, SRX Series firewalls cannot directly share threat intelligence with third party tools. You need to use the Juniper ATP Cloud as the intermediary for threat intelligence sharing. Therefore, the correct answer is B and C. You need to enable Juniper ATP Cloud to share threat intelligence and configure application tokens in the Juniper ATP Cloud to limit who has access.
To do so, you need to perform the following steps:
Enable and configure the TAXII service in the Juniper ATP Cloud. TAXII (Trusted Automated eXchange of Indicator Information) is a protocol for communication over HTTPS of threat information between parties.
STIX (Structured Threat Information eXpression) is a language used for reporting and sharing threat information using TAXII. Juniper ATP Cloud can contribute to STIX reports by sharing the threat intelligence it gathers from file scanning. Juniper ATP Cloud also uses threat information from STIX reports as well as other sources for threat prevention2. To enable and configure the TAXII service, you need to select Configure > Threat Intelligence Sharing in the Juniper ATP Cloud WebUI, move the knob to the right to Enable TAXII, and move the slidebar to designate a file sharing threshold2. Configure application tokens in the Juniper ATP Cloud. Application tokens are used to authenticate and authorize requests to the Juniper ATP Cloud API and the TAXII service. You can create and manage application tokens in the Juniper ATP Cloud WebUI by selecting Configure > Application Tokens. You can specify the name, description, expiration date, and permissions of each token. You can also revoke or delete tokens as needed. You can use the application tokens to limit who has access to your shared threat intelligence by granting or denying permissions to the TAXII service1.
Reference: Threat Intelligence Open API Setup Guide
Configure Threat Intelligence Sharing
About Juniper Advanced Threat Prevention Cloud
NEW QUESTION # 67
You have deployed an SRX Series device at your network edge to secure Internet-bound sessions for your local hosts using source NAT. You want to ensure that your users are able to interact with applications on the Internet that require more than one TCP session for the same application session.
Which two features would satisfy this requirement? (Choose two.)
- A. double NAT
- B. STUN
- C. address persistence
- D. persistent NAT
Answer: C,D
Explanation:
Address persistence ensures that the same NAT IP address is used for all sessions originating from a single source IP. Persistent NAT maintains connections for applications needing multiple sessions, like VoIP.
Additional details are available in Juniper NAT Documentation.
For applications that require multiple TCP sessions for the same application session (such as VoIP or certain online games), the SRX device needs to handle NAT properly to maintain session continuity. Here's what helps:
* Address Persistence (Answer A): Address persistence ensures that multiple sessions initiated by the same internal host are mapped to the same external IP address. This is crucial for applications that use multiple TCP sessions to maintain a stateful connection with the external server.
Command Example:
bash
Copy code
set security nat source persistent-nat address-persistence
* Persistent NAT (Answer C): This feature allows the external server to initiate new connections to the internal client using the same NAT translation. It's essential for applications that require consistent NAT mappings across multiple sessions.
Command Example:
bash
Copy code
set security nat source persistent-nat permit target-host-port
These features ensure that applications with multiple TCP sessions work seamlessly across NAT.
NEW QUESTION # 68
You are enabling advanced policy-based routing. You have configured a static route that has a next hop from the inet.0 routing table. Unfortunately, this static route is not active in your routing instance.
In this scenario, which solution is needed to use this next hop?
- A. Use policies.
- B. Use RIB groups.
- C. Use transparent mode.
- D. Use filter-based forwarding.
Answer: B
Explanation:
To enable advanced policy-based routing in Junos OS and activate a static route with a next-hop address in the inet.0 table within your routing instance, you should utilize RIB groups. RIB groups allow you to import routes from one routing table to another. In this scenario, the static route within the routing instance needs access to the inet.0 routes, which is facilitated by configuring a RIB group. Juniper's documentation outlines RIB groups as a necessary component for handling instances where routes need to be shared across routing tables, thereby ensuring seamless traffic flow through specified routes. For more details, refer to the Juniper Networks Documentation on RIB Groups.
NEW QUESTION # 69
You have deployed automated threat mitigation using Security Director with Policy Enforcer, Juniper ATP Cloud, SRX Series devices, Forescout, and third-party switches.
In this scenario, which device is responsible for communicating directly to the third-party switches when infected hosts need to be blocked?
- A. Juniper ATP Cloud
- B. Policy Enforcer
- C. Forescout
- D. SRX Series device
Answer: C
Explanation:
In the described scenario, Forescout is responsible for communicating with the third-party switches to enforce mitigation actions when infected hosts are detected. Forescout integrates with Policy Enforcer and other network security products to provide dynamic network access control. When an infected host is detected by Juniper ATP Cloud or SRX devices, Forescout interacts with the switches to enforce the quarantine or block policy, ensuring that the compromised device is isolated from the network.
Forescout manages the access control lists (ACLs) or other blocking mechanisms on the third-party switches, while Policy Enforcer coordinates with different systems like SRX devices and ATP Cloud for real-time threat mitigation.
NEW QUESTION # 70
Referring to the exhibit, you have been assigned the user LogicalSYS1 credentials shown in the configuration.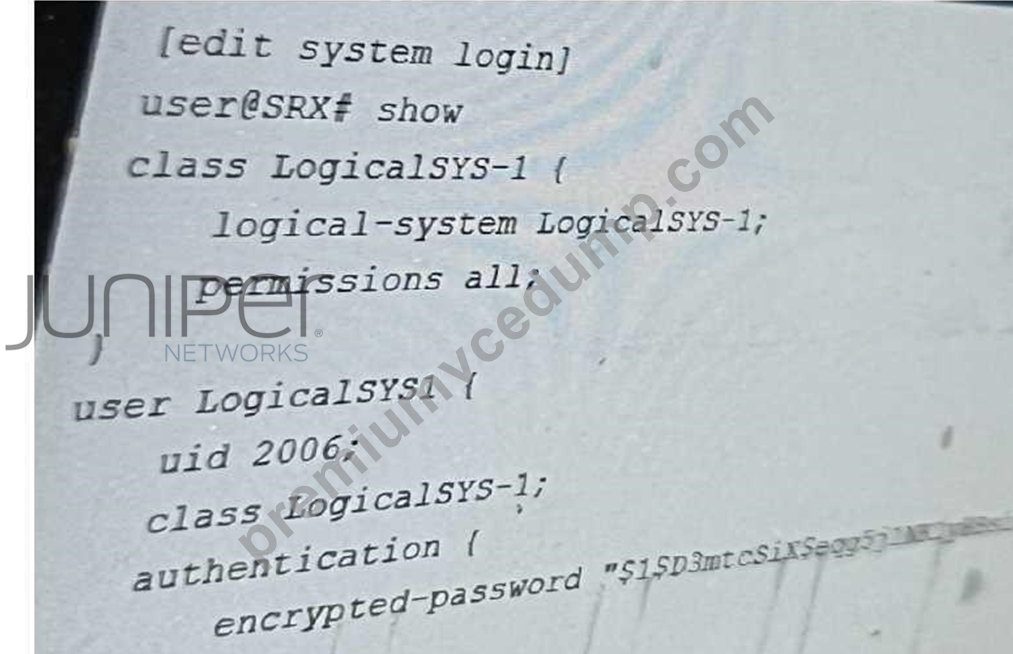
In this scenario, which two statements are correct? (Choose two.)
- A. When you log in to the device, you will be located at the operational mode of the Logic
- B. When you log in to the device, you will be located at the operational mode of the main system
- C. When you log in to the device, you will be permitted to view all routing tables available on the SRX device
- D. When you log in to the device, you will be permitted to view only the routing tables for Logic
Answer: A,D
NEW QUESTION # 71
You are requested to enroll an SRX Series device with Juniper ATP Cloud.
Which statement is correct in this scenario?
- A. If a device is already enrolled in a realm and you enroll it in a new realm, the device data or configuration information is propagated to the new realm.
- B. Juniper ATP Cloud uses a Junos OS op script to help you configure your SRX Series device to connect to the Juniper ATP Cloud service.
- C. The only way to enroll an SRX Series device is to interact with the Juniper ATP Cloud Web portal.
- D. When the license expires, the SRX Series device is disenrolled from Juniper ATP Cloud without a grace period
Answer: B
NEW QUESTION # 72
You must implement an IPsec VPN on an SRX Series device using PKI certificates for authentication.
As part of the implementation, you are required to ensure that the certificate submission, renewal, and retrieval processes are handled automatically from the certificate authority.
In this scenario, which statement is correct.
- A. You can use SPKI to accomplish this behavior.
- B. You can use OCSP to accomplish this behavior.
- C. You can use SCEP to accomplish this behavior.
- D. You can use CRL to accomplish this behavior.
Answer: C
Explanation:
Certificate Renewal
The renewal of certificates is much the same as initial certificate enrollment except you are just replacing an old certificate (about to expire) on the VPN device with a new certificate. As with the initial certificate request, only manual renewal is supported. SCEP can be used to re-enroll local certificates automatically before they expire. Refer to Appendix D for more details.
NEW QUESTION # 73
Click the Exhibit button.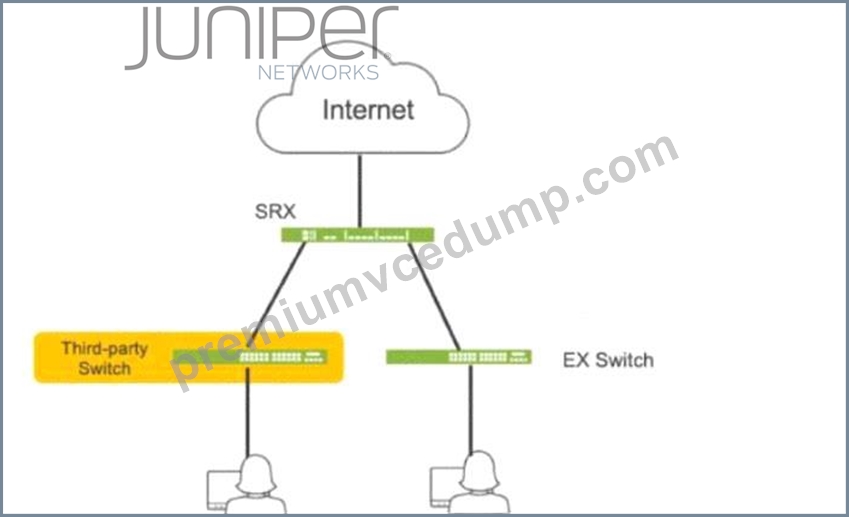
Referring to the exhibit, which three actions do you need to take to isolate the hosts at the switch port level if they become infected with malware? (Choose three.)
- A. Use a third-party connector.
- B. Enroll the SRX Series device with Juniper ATP Cloud.
- C. Deploy Security Director with Policy Enforcer.
- D. Configure AppTrack on the SRX Series device.
- E. Deploy Juniper Secure Analytics.
Answer: B,C,D
Explanation:
To isolate hosts at the switch port level when they become infected with malware, the SRX Series device must integrate with advanced threat detection and network management tools. Here's how the actions contribute to achieving this:
* Explanation of Answer A (Enroll SRX with Juniper ATP Cloud):
* Enrolling the SRX Series device withJuniper ATP Cloudallows for advanced malware detection and prevention. Juniper ATP (Advanced Threat Prevention) Cloud provides a cloud-based sandboxing solution that analyzes files and traffic for malicious behavior, helping to identify infected hosts.
* Once the SRX is enrolled, it can receive real-time threat intelligence from the cloud, enabling proactive isolation of compromised hosts.
* Explanation of Answer C (Deploy Security Director with Policy Enforcer):
* Security DirectorwithPolicy Enforcerallows for centralized security management and automated responses. Policy Enforcer can dynamically update policies to block infected hosts and isolate them based on detected threats. This is critical for automating the isolation process at the switch port level.
* With Policy Enforcer, you can quarantine infected devices automatically.
* Explanation of Answer D (Configure AppTrack on SRX):
* AppTrackis used to monitor and track application usage on the network. By configuring AppTrack on the SRX, you can detect abnormal behavior that may indicate malware infections, such as unusual application usage patterns. AppTrack can also generate logs and alerts to assist in isolating infected hosts at the switch port level.
* This provides visibility into which applications are being used, helping to identifymalicious traffic.
Juniper Security Reference:
* Juniper ATP Cloud Overview: Integrates advanced malware detection and threat intelligence for proactive defense.
* Security Director with Policy Enforcer: Automates policy changes in response to threats, ensuring fast isolation of infected hosts. Reference: Juniper Security Director Documentation.
* AppTrack: Provides application visibility, monitoring, and threat detection. Reference: Juniper AppTrack Documentation.
NEW QUESTION # 74
A company has acquired a new branch office that has the same address space of one of its local networks,
192.168.100/24. The offices need to communicate with each other.
Which two NAT configurations will satisfy this requirement? (Choose two.)
- A. [edit security nat static]
user@OfficeB# show rule-set From-Office-A {
from interface ge-0/0/0.0;
rule 1 {
match {
destination-address 192.168.210.0/24;
}
then {
static-nat {
prefix 192.168.100.0/24;
}
}
}
} - B. [edit security nat static]
user@OfficeA# show rule-set From-Office-B {
from interface ge-0/0/0.0;
rule 1 {
match {
destination-address 192.168.200.0/24;
}
then {
static-nat {
prefix 192.168.100.0/24;
}
}
}
} - C. [edit security nat source]
user@OfficeA# show rule-set OfficeBtoA {
from zone OfficeB;
to zone OfficeA;
rule 1 {
match {
source-address 192.168.210.0/24;
destination-address 192.168.200.0/24;
}
then {
source-nat {
interface;
}
}
}
} - D. [edit security nat source]
user@OfficeB# show rule-set OfficeAtoB {
from zone OfficeA;
to zone OfficeB;
rule 1 {
match {
source-address 192.168.200.0/24;
destination-address 192.168.210.0/24;
}
then {
source-nat {
interface;
}
}
}
}
Answer: C,D
Explanation:
The problem describes two offices needing to communicate, but both share the same IP address space,
192.168.100.0/24. To resolve this, NAT must be configured to translate the conflicting address spaces on each side. Here's how each of the configurations works:
* Option A (Correct):This source NAT rule translates the source address of traffic fromOffice Bto Office A. By configuring source NAT, the source IP addresses from Office B (192.168.210.0/24) will be translated when communicating with Office A (192.168.200.0/24). This method ensures that there is no overlap in address space when packets are transmitted between the two offices.
* Option D (Correct):This is a source NAT rule configured onOffice B, which translates the source addresses fromOffice Ato prevent address conflicts. It ensures that when traffic is initiated fromOffice AtoOffice B, the overlapping address range (192.168.100.0/24) is translated.
* Options B and C (Incorrect):These options involve static NAT rules that map address ranges between the two offices, but they do not resolve the overlapping IP address space issue effectively. Static NAT is not the optimal solution in this scenario since the problem involves address space conflict, which requires translation of source addresses during communication.
Juniper References:
* Juniper NAT Configuration Guide: Detailed instructions on how to configure source NAT and resolve address conflicts between networks.
NEW QUESTION # 75
Exhibit
Referring to the exhibit, which three protocols will be allowed on the ge-0/0/5.0 interface? (Choose three.)
- A. IBGP
- B. NTP
- C. OSPF
- D. IPsec
- E. DHCP
Answer: B,C,D
NEW QUESTION # 76
Exhibit: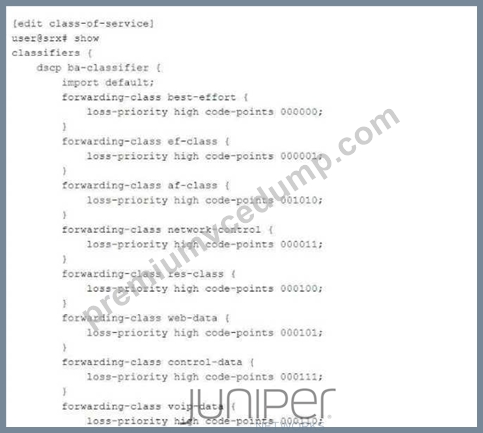
You have configured a CoS-based VPN that is not functioning correctly. Referring to the exhibit, which action will solve the problem?
- A. You must change the code point for the DB-data forwarding class to 10000.
- B. You must change the loss priorities of the forwarding classes to low.
- C. You must delete one forwarding class.
- D. You must use inet precedence instead of DSCP.
Answer: C
Explanation:
In the exhibit, the CoS-based VPN configuration is not functioning correctly due to an issue with the number of forwarding classes. The maximum number of forwarding classes supported for CoS-based VPNs with multiple SAs (security associations) is typically four forwarding classes. In this case, more than four forwarding classes are defined.
To solve the issue, one forwarding class must be deleted to ensure that the total number of forwarding classes is reduced to four or fewer.
NEW QUESTION # 77
You want to enforce I DP policies on HTTP traffic.
In this scenario, which two actions must be performed on your SRX Series device? (Choose two)
- A. Disable screen options on the Untrust zone.
- B. Match on application junos-http.
- C. Specify an action of None.
- D. Choose an attacks type in the predefined-attacks-group HTTP-All.
Answer: B,D
NEW QUESTION # 78
Which two statements are correct about automated threat mitigation with Security Director?(Choose two.)
- A. Infected hosts are tracked by their MAC address.
- B. Infected hosts are tracked by their chassis serial number.
- C. Infected hosts are tracked by their user identity.
- D. Infected hosts are tracked by their IP address.
Answer: C,D
Explanation:
Security Director provides an integrated security management solution for Juniper devices, including SRX Series Firewalls. Automated threat mitigation refers to the system's capability to react dynamically to security incidents such as malware infections, based on predefined policies. Let's dive into the details behind each selected option:
* IP Address Tracking (Correct: Option A):Infected hosts are tracked by their IP address because the firewall and threat mitigation systems use the IP address as a key identifier for network traffic and routing. IP addresses are fundamental in identifying which device on the network is exhibiting malicious behavior. Security Director can automatically track and block these infected hosts using their IP addresses by correlating threat logs and incident data with a specific device's network activities.
* User Identity Tracking (Correct: Option D):Security Director integrates with identity management solutions and LDAP directories to correlate security incidents with specific user identities. This capability allows the security system to track threats not only by device but also by the authenticated user currently associated with that device. This feature is particularly useful in environments where multiple users share devices, or where network access is granted based on user credentials.
Now, let's discuss why the other options are incorrect:
* MAC Address Tracking (Incorrect: Option C):While MAC addresses can be used for identifying devices on the same local network, they are not a primary tracking method for infected hosts in the broader network managed by Security Director. MAC addresses are not visible once traffic passes through routers since Layer 2 information is stripped off. Therefore, Juniper's automated threat mitigation focuses more on IP and user identity tracking rather than MAC addresses.
* Chassis Serial Number Tracking (Incorrect: Option B):Tracking infected hosts by chassis serial number is not a common practice in automated threat mitigation. Serial numbers are primarily used for inventory and hardware management purposes, rather than for identifying infected hosts or mitigating threats in real time.
Juniper References:
* Juniper Security Director Documentation explains how IP addresses and user identities are tracked for threat mitigation, highlighting the importance of dynamic response based on these identifiers.
* Security Director supports dynamic blocklists and real-time mitigation strategies based on both IP and user-based tracking, leveraging integration with Active Directory (AD) or LDAP for identity-based policies.
NEW QUESTION # 79
......
Exam Questions for JN0-637 Updated Versions With Test Engine: https://pass4lead.premiumvcedump.com/Juniper/valid-JN0-637-premium-vce-exam-dumps.html